OpenSSL Verify Signed Documents with RSA Keys
What is the process of verifying the signed document with RSA keys using OpenSSL commands? I received a signed document and was to verify it with senders RSA public key.
✍: FYIcenter.com
 Here are steps your need to follow to verify a signed document with sender's RSA public key
using OpenSSL commands:
1. Verify that you received 3 files from the sender: the document file, the signature file and the RSA public key file.
2. Generate a new digest string from the document using the same algorithm used by the sender.
3. Decrypt the old digest string from the signature file using the RSA public key.
4. Compare the new digest string with the old digest string.
5. If digest strings match with each other, the document signature is valid.
5. If digest strings do not match with each other, the document signature is invalid.
The diagram below shows you the document signature verifying process:
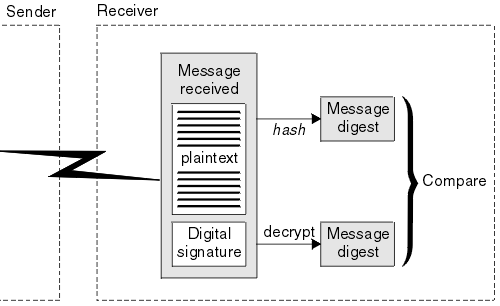
⇒ OpenSSL "rsautl -verify" - RSA Signature Verification
⇐ OpenSSL "rsautl -sign" - RSA Signature Generation
2017-03-27, ∼3616🔥, 0💬
